lundi 13 avril 2020

Hacking All The Cars - Part 1


A step by step lab based mini course on analyzing your car network


I wanted to learn about hacking cars. As usual I searched around the internet and didn't find any comprehensive resources on how to do this, just bits and pieces of the same info over and over which is frustrating. I am not a car hacking expert, I just like to hack stuff. This mini course will run in a fully simulated lab environment available from open garages, which means in 5 minutes from now you can follow along and hack cars without ever bricking your girlfriends car. Since you obviously wouldn't attack your own Lambo, totally use your girlfriends Prius. 

Below are the topics covered in this blog  series so you can decide if you want to read further: 

Whats covered in this car hacking mini course: 

Setting up Virtual Environments for testing
Sniffing CAN Traffic
Parsing CAN Traffic
Reverse Engineering CAN IDs 
Denial of service attacks
Replaying/Injecting Traffic
Coding your own CAN Socket Tools in python
Targeted attacks against your cars components
Transitioning this to attacking a real car with hardware

The first thing we are going to do before we get into any car hacking specifics such as "WTF is CAN?", is get your lab up and running. We are going to run a simple simulated CAN Bus network which controls various features of your simulated car. Its better to learn by doing then sit here and recite a bunch of car network lingo at you and hope you remember it.  

I also don't want you to buy a bunch of hardware and jack into your real car right away. Instead there are options that can get you started hacking cars RIGHT NOW by following along with this tutorial. This will also serve to take away the fear of hacking your actual car by understanding what your doing first. 


Video Playlist: 


Setting up your Lab: 

First things first, set yourself up with an Ubuntu VMware install, and load it up. Optionally you could use a Kali Iinux VM, however, that thing drives me nuts with copy paste issues and I think Kayak was giving me install problems. So support is on you if you would like to use Kali. However, I do know Kali will work fine with OpenGarages virtual car.. So feel free to use it for that if you have it handy and want to get started right away. 


Install PreReq Libraries: 

Once you load this up you are going to want to install CAN utilities and pre-requisite libraries. This is really easy to do with the following Apt-get commands:
sudo apt-get update
sudo apt-get install libsdl2-dev libsdl2-image-dev can-utils  

Then we are going to pull down the ICSimulator repo: 


Starting the simulator: 

Once this is done we can startup the simulator by changing directories to the downloaded repo and running the following 2 commands, which will setup a virtual CAN interface and a simulator GUI Cluster: 

Run the setup Script to get the vcan0 interface up: 
root@kali:~/ICSim# ./setup_vcan.sh 
root@kali:~/ICSim# ./icsim vcan0

On a new terminal tab we will open up our simulators controller with the following command,
root@kali:~/ICSim#./controls vcan0

Note: that the controller must be the in-focus GUI screen to send keyboard commands to the simulator. 


How to Use the Simulator: 

The simulator has a speedometer with Right and Left turn signals, doors etc.  Below are the list of commands to control the simulator when the Control panel is in focus. Give them each a try and note the changes to the simulator. 
Up and Down keys control the gauges clusters speedometer
Left and Right keys Control the Blinkers
Right Shift + X, A or B open doors 
Left Shift + X, A or be Close doors

Try a few of the above commands for example Right Shift +X and you will see the interface change like so, notice the open door graphic: 


Awesome, thanks to OpenGarages you now you have your very own car to hack

Notice in the setup commands above we used a VCan0 interface. Run Ifconfig and you will now see that you indeed have a new network interface that speaks to the CAN network over VCan0. 

ficti0n@ubuntu:~/Desktop/ICSim$ ifconfig vcan0
vcan0     Link encap:UNSPEC  HWaddr 00-00-00-00-00-00-00-00-00-00-00-00-00-00-00-00  
          UP RUNNING NOARP  MTU:16  Metric:1
          RX packets:558904 errors:0 dropped:0 overruns:0 frame:0
          TX packets:558904 errors:0 dropped:0 overruns:0 carrier:0
          collisions:0 txqueuelen:1 
          RX bytes:3663935 (3.6 MB)  TX bytes:3663935 (3.6 MB)


Car networks run on a variety of protocols most prevalent being CAN. You can think of a CAN Bus like an old school networking hub where everyone can see everyone elses traffic. This is true to some extent although you may not see all of the cars traffic if its not connected to that particular bus your plugged into. You can think of CAN traffic kind of like UDP in that its send and forget, the main difference being parts of the CAN bus network don't actually have addresses and everything runs off arbitration IDs and priorities. Thats enough background to get you doing rather then reading.

With a little knowledge out of the way lets check if we can see our CAN traffic from our virtual car via the CanDump utility, which you installed as part of CanUtils package above. Using the following command on the vcan0 interface our simulator uses you can view a stream of traffic: 

ficti0n@ubuntu:~/Desktop/ICSim$ candump vcan0


Above we can see a bunch of CAN frames, and if we perform actions on the vehicle we will see changes to data values in the CanDump output.  However this may happen very fast, and we may not be able to see if for example we unlocked our simulators door. This is because things are changing constantly in the cars IDLE state. One single value changing may not stand out enough for us to take notice or may scroll so fast we cant see it. 


Capture and Replay CAN Actions: 

One option would be to perform an action and replay it, we should see the actions happen again in the replay if the traffic for the action we recorded is on the same bus network our device is plugged into. There are loads of networks within a car and its not guaranteed our network tap for example an OBD2 port plugin is connected to the same network as door we opened.  Or the door may not be connected to the network at all depending on your car and its age or how its configured. 

Replaying dumps with CanPlayer: 
Another useful tool included with CanUtils package is CanPlayer for replaying traffic. If the functionality we are trying to capture is on the same Bus as the adaptor plugged into the car, or in this case our Virtual CAN interface, we can use CanDump to save traffic to a file. We then use CanPlayer to replay the traffic on the network. For example lets run CanDump and open a door and then replay the functionality with CanPlayer. 

Lab 1 Steps: 

  1. Run CanDump
  2. Right Shift + X to open a door
  3. Cancel CanDump (ctrl+c)
  4. Left Shift + X to close the door
  5. Run can player with the saved dump and it will replay the traffic and open the door

Recording the door opening:  (-l for logging) 
ficti0n@ubuntu:~/Desktop/ICSim$ candump -l vcan0

Replaying the CanDump file:  (use the file your can dump created) 
ficti0n@ubuntu:~/Desktop/ICSim$ canplayer -I candump-2018-04-06_154441.log 

Nice, so if all went well you should see that your door is now open again. If this did not happen when attacking a real car, just try to replay it again. CAN networks are not like TCP/IP, they are more like UDP in that you send out your request and its not expecting a response. So if it gets lost then it gets lost and you have to resend. Perhaps something with higher priority on the network was sending at the time of your replay and your traffic was overshadowed by it.   


Interacting with the Can Bus and Reversing Traffic: 

So thats cool, but what about actually understanding what is going on with this traffic, CanDump is not very useful for this, is scrolls by to quickly for us to learn much from.  Instead we can use CanSniffer with colorized output to show us the bytes within packets that change. Below is an example of CanSniffer Traffic: 

To startup can sniffer run the following: 
ficti0n@ubuntu:~/Desktop/ICSim$ cansniffer -c vcan0
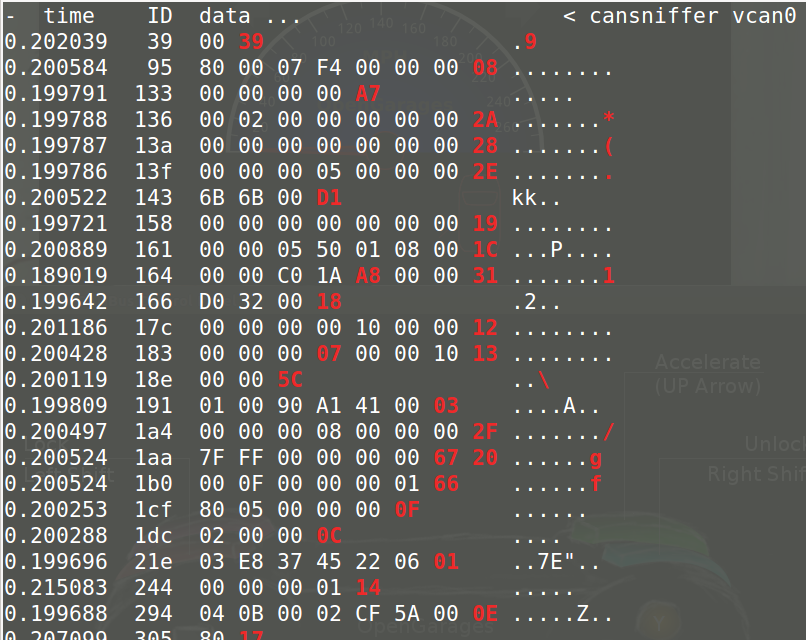


You will see 3 fields, Time, ID  and Data. Its pretty easy to figure out what these are based on thier name. The most important part for our usage in this blog are the ID and the Data fields.  

The ID field is the frame ID which is loosely associated with the device on the network which is effected by the frame being sent. The ID to also determines the priority of the frame on the network.  The lower the number of the CAN-ID the higher priority it has on the network and more likely it will be handled first.  The data field is the data being sent to change some parameter like unlocking a door or updating output. You will notice that some of the bytes are highlighted RED. The values in red are the values that are changing during the idle state you are currently in. 


Determine which ID and Byte controls the throttle: 

So with the terminal sniffing window open put the simulator and the controller into the foreground, with the controller being the window you have clicked and selected.  Pay attention to the CanSniffer output while hitting the UP ARROW and look for a value that was white but is now Red and increasing in value as the throttle goes up.  This might take you a few minutes of paying attention to whats going on to see. 

The following 2 pictures show ID 244 in the IDLE state followed by pressing the up button to increase the speed. You will notice a byte has turned red and is increasing in value through a range of HEX values 0-F. It will continue to enumerate through values till it reaches its max speed. 


The byte in ID 244 which is changing is the value while the throttle is engaged, so 244 associated in some way with the increasing speed.   The throttle speed is a good value to start with as it keeps increasing its value when pressed making it easier to spot while viewing the CanSniffer output.  


Singling out Values with Filters: 

If you would like to single out the throttle value then click the terminal window and press -000000 followed by the Enter key which will clear out all of the values scrolling. Then press +244 followed by the Enter key which will add back the throttle ID. You can now click the controller again and increase the speed with your Up arrow button without all the noise clouding your view.  You will instead as shown below only have ID 244 in your output: 


To get back all of the IDs again click the terminal window and input +000000 followed by the Enter key.   Now you should see all of the output as before.  Essentially 000000 means include everything. But when you put a minus in front of it then it negates everything and clears your terminal window filtering out all values. 


Determine Blinker ID: 

Now lets figure out another ID for the blinkers. If you hit the left or right arrow with the controls window selected you will notice a whole new ID appears in the list, ID 188 shown in the picture below which is associated with the blinker. 


This ID was not listed before as it was not in use within the data output until you pressed the blinker control.  Lets single this value out by pressing -000000 followed by +188.  Just like in the throttle example your terminal should only show ID 188, initially it will show with 00 byte values. 

 As you press the left and the right blinker you will see the first Byte change from 00 to 01 or 02. If neither is pressed as in the screenshot above it will be 00. Its kind of hard to have the controller in focus and get a screenshot at the same time but the ID will remain visible as 00 until it times out and disappears from the list when not active. However with it filtered out as above you can get a better view of things and it wont disappear.  


Time for YOU to do some Protocol Reversing:

This lab will give you a good idea how to reverse all of the functionality of the car and associate each action with the proper ID and BYTE. This way you can create a map of intended functionality changes you wish to make.  Above we have done a few walk throughs with you on how to determine which byte and ID is associated with an action. Now its time to map everything out yourself with all the remaining functionality before moving on to attacking individual components.  


Lab Work Suggestion: 


  1. Take out a piece of paper and a pencil
  2. Try unlocking and locking doors and write down the ID which controls this action (remember your filters)
  3. Try unlocking each door and write down the BYTES needed for each door to open
  4. Try locking each doors and what Bytes change and what are their values, write them down
  5. Do the same thing for the blinkers left and right (Might be different then what I did above) 
  6. What ID is the speedometer using?  What byte changes the speed? 


Attacking Functionality Directly: 

With all of the functionality mapped out we can now try to target various devices in the network directly without interacting with the controllers GUI. Maybe we broke into the car via cellular OnStar connection  or the center console units BLE connection which was connected to the CAN network in some way.  
After an exploit we have direct access to the CAN network and we would like to perform actions. Or maybe you have installed a wireless device into an OBD2 port under the dashboard you have remote access to the automobile. 

Using the data from the CAN network reversing lab above we can call these actions directly with the proper CAN-ID and Byte.  Since we are remote to the target we can't just reach over and grab the steering wheel or hit the throttle we will instead send your CAN frame to make the change.
One way we can do this is via the CanSend utility. Lets take our information from our lab above and make the left turn signal flash with the following ID 188 for the turn signal by changing the first byte to 01 indicating the left signal is pressed. CanSend uses the format ID#Data. You will see this below when sending the turn signal via CanSend. 

ficti0n@ubuntu:~/Desktop/ICSim$ cansend vcan0 188#01000000 


You should have noticed that the left signal flashed. If not pay more attention and give it another try or make sure you used the correct ID and changed the correct byte.  So lets do the same thing with the throttle and try to set the speed to something with ID 244 that we determined was the throttle. 

ficti0n@ubuntu:~/Desktop/ICSim$ cansend vcan0 244#00000011F6 

My guess is that nothing happened because its so fast the needle is not going to jump to that value. So instead lets try repeating this over and over again with a bash loop which simply says that while True keep sending the throttle value of 11 which equates to about 30mph: 

ficti0n@ubuntu:~/Desktop/ICSim$ while true; do cansend vcan0 244#00000011F6;  done


Yes thats much better, you may notice the needle jumping back and forth a bit. The reason the needle is bouncing back and forth is because the normal CAN traffic is sent telling the car its actually set to 00 in between your frames saying its 30mph.  But it worked and you have now changed the speed the car sees and you have flashed the blinker without using the cars normal blinker controls. Pretty cool right? 


Monitor the CAN Bus and react to it: 

Another way to handle this issue is to monitor the CAN network and when it sees an ID sent it will automatically send the corresponding ID with a different value.. Lets give that a try to modify our speed output by monitoring for changes. Below we are simply running CanDump and parsing for ID 244 in the log output which is the throttle value that tells the car the speed. When a device in the car reports ID 244 and its value we will immediately resend our own value saying the speed is 30mph with the value 11.  See below command and try this out. 

ficti0n@ubuntu:~/Desktop/ICSim$ candump vcan0 | grep " 244 " | while read line; do cansend vcan0 244#00000011F6; done

With this running after a few seconds you will see the speed adjust to around 30MPH once it captures a legitimate CAN-ID 244 from the network traffic and sends its own value right after.  

Ok cool, so now while the above command is still running click the controller window and start holding down the Up arrow with the controller in focus.. After a few seconds or so when the speed gets above 30MPH you will see the needle fighting for the real higher value and adjusting back to 30MPH as your command keeps sending its on value as a replacement to the real speed. 

So thats one way of monitoring the network and reacting to what you see in a very crude manner.  Maybe someone stole your car and you want to monitor for an open door and if they try to open the door it immediately locks them in. 


Conclusion and whats next: 

I am not an expert car hacker but I hope you enjoyed this. Thats about as far as I want to go into this subject today, in the next blog we will get into how to code python to perform actions on the CAN network to manipulate things in a similar way.  With your own code you are not limited to the functionality of the tools you are provided and can do whatever you want. This is much more powerful then just using the CanUtils pre defined tools. Later on I will also get into the hardware side of things if you would like to try this on a real car where things are more complicated and things can go wrong. 

Related posts

Group Instant Messaging: Why Blaming Developers Is Not Fair But Enhancing The Protocols Would Be Appropriate

After presenting our work at Real World Crypto 2018 [1] and seeing the enormous press coverage, we want to get two things straight: 1. Most described weaknesses are only exploitable by the malicious server or by knowing a large secret number and thereby the protocols are still very secure (what we wrote in the paper but some newspapers did not adopt) and 2. we see ways to enhance the WhatsApp protocol without breaking its features.


We are of course very happy that our research reached so many people and even though IT security and cryptography are often hard to understand for outsiders, Andy Greenberg [2], Patrick Beuth [3] and other journalists [4,5,6,7,8] wrote articles that were understandable on the one hand and very accurate and precise on the other hand. In contrast to this, we also saw some inaccurate articles [9,10] that fanned fear and greatly diverged in their description from what we wrote in our paper. We expected this from the boulevard press in Germany and therefore asked them to stick to the facts when they were contacting us. But none of the worst two articles' [9,10] authors contacted us in advance. Since our aim was never to blame any application or protocol but rather we wanted to encourage the developers to enhance the protocols, it contradicts our aim that WhatsApp and Signal are partially declared attackable by "anyone" "easily" [9,10].

Against this background, we understand Moxie's vexation about certain headlines that were on the Internet in the last days [11]. However, we believe that the ones who understand the weaknesses, comprehend that only the malicious server can detectably make use of them (in WhatsApp) or the secret group ID needs to be obtained from a member (in Signal). As such, we want to make clear that our paper does not primarily focus on the description of weaknesses but presents a new approach for analyzing and evaluating the security of group instant messaging protocols. Further we propose measures to enhance the analyzed protocols. The description of the protocols' weaknesses is only one part of the evaluation of our analysis approach and thereby of the investigation of real world protocols. This is the scientific contribution of our paper. The practical contribution of the analyzed messengers, which is the communication confidentiality for billion users (in most cases), is great and should be noted. Therefore we believe that being Signal, WhatsApp, or Threema by applying encryption to all messages and consequently risking research with negative results is much better than being a messenger that does not encrypt group messages end-to-end at all. We do not want to blame messengers that are far less secure (read Moxie's post [11] if you are interested).

Finally we want note that applying security measures according to the ticket approach (as we call it in the paper [12]) to the invitation links would solve the issues that Facebook's security head mentioned in his reply [13] on our findings. To our knowledge, adding authenticity to group update messages would not affect invitation links: If no invitation link was generated for a group, group members should only accept joining users if they were added by an authentic group update message. As soon as a group invitation link was generated, all joining users would need to be accepted as new group members with the current design. However there are plenty ways how WhatsApp could use invitation links without endowing the server with the power to manage groups without the group admins' permission:
One approach would be generating the invitation links secretly and sharing them without the knowledge of the server. An invitation link could then contain a secret ticket for the group and the ID of the group. As soon as a user, who received the link, wants to join the group, she can request the server with the group ID to obtain all current group members. The secret ticket can now be sent to all existing group members encrypted such that the legitimate join can be verified.

Of course this would require engineering but the capability of WhatsApp, shipping drastic protocol updates, can be assumed since they applied end-to-end encryption in the first place.

[1] https://www.youtube.com/watch?v=i5i38WlHfds
[2] https://www.wired.com/story/whatsapp-security-flaws-encryption-group-chats/
[3] http://www.spiegel.de/netzwelt/apps/whatsapp-gruppenchats-schwachstelle-im-verschluesselungs-protokoll-a-1187338.html
[4] http://www.sueddeutsche.de/digital/it-sicherheit-wie-fremde-sich-in-whatsapp-gruppenchats-einladen-koennen-1.3821656
[5] https://techcrunch.com/2018/01/10/security-researchers-flag-invite-bug-in-whatsapp-group-chats/
[6] http://www.telegraph.co.uk/technology/2018/01/10/whatsapp-bug-raises-questions-group-message-privacy/
[7] http://www.handelsblatt.com/technik/it-internet/verschluesselung-umgangen-forscher-finden-sicherheitsluecke-bei-whatsapp/20836518.html
[8] https://www.heise.de/security/meldung/WhatsApp-und-Signal-Forscher-beschreiben-Schwaechen-verschluesselter-Gruppenchats-3942046.html
[9] https://www.theinquirer.net/inquirer/news/3024215/whatsapp-bug-lets-anyone-easily-infiltrate-private-group-chats
[10] http://www.dailymail.co.uk/sciencetech/article-5257713/WhatsApp-security-flaw-lets-spy-private-chats.html
[11] https://news.ycombinator.com/item?id=16117487
[12] https://eprint.iacr.org/2017/713.pdf
[13] https://twitter.com/alexstamos/status/951169036947107840

Further articles:
- Matthew Green's blog post: https://blog.cryptographyengineering.com/2018/01/10/attack-of-the-week-group-messaging-in-whatsapp-and-signal/
- Schneier on Security: https://www.schneier.com/blog/archives/2018/01/whatsapp_vulner.html
- Bild: http://www.bild.de/digital/smartphone-und-tablet/whatsapp/whatsapp-sicherheitsluecke-in-gruppenchats-54452080.bild.html
- Sun: https://www.thesun.co.uk/tech/5316110/new-whatsapp-bug-how-to-stay-safe/

More info


  1. Pentest Tools Free
  2. Hacking Tools Online
  3. Easy Hack Tools
  4. Hacker Tools Apk Download
  5. Hack Tool Apk No Root
  6. Hacking Tools 2019
  7. Hacker Search Tools
  8. Hacker Tools Linux
  9. Pentest Tools Website
  10. Black Hat Hacker Tools
  11. Hacking Tools Pc
  12. What Are Hacking Tools
  13. Pentest Tools Nmap
  14. Best Hacking Tools 2019
  15. Pentest Tools Online
  16. Hacking Tools Windows 10
  17. Hackrf Tools
  18. Hack Website Online Tool
  19. Hacker Tools Software
  20. Hack And Tools

samedi 11 avril 2020

Movie Review: Avengers: Endgame (SPOILERS)

Probably the best thing about Endgame is that it's the (almost) last of the first generation of MCU movies (we still have a Spiderman movie, maybe a Black Widow movie, and I'm sure a whole 'other next-generation of MCU movies are in the works). Is it a good movie? No. Is it a good-MCU movie? It's fine, much in the same way that Harry Potter 8 was fine: it does what it is supposed to.

That it broke box office records is understandable since the last movie was a cliff-hanger. Less understandable is its rave reviews, unless the reviews are based on its "must see" quality. Because, even from a Marvel perspective, the movie just barely makes sense, is disjointed, has too many scenes that are just sketches, has too many underused characters, and has an ending that is somewhat anti-climactic. What it has going for it is some emotional impact (a bit), some humor (not all of it good), some flashbacks to previous MCU movies, some nice visuals, and a sense of an ending.

PLOT: Following the last movie where half of the universe is wiped out, the characters are upset. The survivors track down Thanos who has already destroyed the stones so that his work can't be undone, so all they can do is kill him. Five years later Ant-Man is accidentally rescued from the quantum realm but has experienced only 5 hours, which leads him to think that the Avengers can use the quantum realm to go back in time - and space (???) - to very specific times and places in order to steal the infinity stones from the past, undo what Thanos did, and return them to their timelines. Unfortunately, while in the past, future Nebula's presence and memories alert past Thanos to this plan and he travels into the present to destroy the universe and remake a new one that won't try this plan again.

REACTIONS: Let's put a pin onto the obvious time-travel paradox problems, and even the rest of the insane problems for one minute and take the movie as is. This movie takes a little time to show us Hawkeye's family, Iron Man's daughter, and a few other character-relationship moments, which is a little more than we get in most MCU movies and which was nice. There was at least some attempt to deal with the failure and loss of the last movie, although, other than an argument from Iron Man and a sense of purpose from Captain America, these attempts were laughably badly done. Thor's gut belly and indifference was supposed to be funny, but other than the quick visual punch it really wasn't. On the one hand it was nice to see an overweight superhero. On the other, too many jokes were made about him being out of shape.

Now we have to take the pin out, because this movie's basic plot, premise, and how it deals with what happened is just insane:

  • If you wipe out half of all "living creatures", what about the animals and vegetation?
  • If you wipe our half of all living creatures, far FAR more than half of the remainder are going to die, and pretty soon. Half of all airplane pilots of mid-flight airplanes and half of the air-traffic controllers are gone. That's thousands of crashed flights. Half of all drivers of cars and trucks are gone but their cars are still speeding. That stops EVERY car and truck on the road, killing millions of people and instantly blocking every major and minor thoroughfare. Who's left to un-jam the roads? Half of all surgeons are gone mid-operation and nurses mid-care. Half of all single-parents with dependents that can't get help. Half of the people that care for remote villages.
  • How about every religion? How many of them could deal with half of their flock, including their pope or chief or most of their cardinals, dying? No riots? No looting? No new cults or major overthrows? How are the governments still working? How are buildings? How is food and medicine getting delivered, let alone produced and harvested and supplied?
  • How about financial markets and the collapse of industry? How about the collapse of all national security? How about rogue nations and terrorism? How about ...
  • Let's talk about what it would mean then to reintroduce half of the population again five years after the world has moved on without them. Where are they reintroduced into the world, including the ones that were mid-flight or mid-driving? Up in the air, at their destination, or at home? Who owns what? Who is married to whom? Who is producing food for them and where do they live?
  • The point is that this kind of disaster is a mcguffin, something that you can't think about even in the most shallow terms because it doesn't make any sense, but the MCU just throws it in and expects you not to think about it.
And that's not even considering the loony ways that time-travel is dealt with, screwing around with multiple timelines with no concept of how to resolve any of the changes. But that consideration is, at least, par for the course for bad sci-fi movies. Also, how does time travel = infinite space travel?

As far as characters go:
  • Iron Man is well acted and has a good show. It was nice to see his callback to the end of the first movie
  • Captain America has definitely grown as a character and had a good show.
  • Black Widow / Hawkeye: yes, it was a better choice for her to die, since he has a real family, but the movie doesn't make you feel that that was more than a plot consideration. Her death was more tragic than Iron Man's, but she is only given a few words of remorse while he is given a whole ending funeral and condolence scene. Which just goes to show that the MCU still doesn't consider the women to be as important as the men.
  • Captain Marvel has barely 15 minutes of screen-time after her big movie. It's entirely unclear how she rescues Iron Man at the beginning. The nice shot of all of the remaining women characters was nice, but it shouldn't be: there are tons of shots of all men characters that we simply take for granted, but the MCU makes us wait for a big, dramatic shot of women characters. I will be more excited when there are so many scenes and shots of women superheroes that we don't notice them anymore.  Which just goes to show that the MCU still doesn't consider the women to be as important as the men.
  • Thanos' powers are never explained. Why would the God of Thunder and several of his weapons have no effect on him, why is he able to break Captain America's unbreakable shield, and why can't even Captain Marvel put a dent in him? Plot, is the only reason. The MCU dug themselves into a hole when they gave superheroes so much strength and then could not think  of a way to create tension without simply ignoring all of that strength. Tension with an overly strong superhero is supposed to come from moral complexity, deception, and self-actualization, not from Something Even Stronger.
  • Hulk: They keep finding new ways to present him to keep him fresh, which is nice. But he's still pretty boring as a character.
  • Ant-Man: I kind of forgot where he was, once the time travelling started. Oh wait, I think I saw him flying around with the Wasp here and there. Whatever.
  • Nebula and Gemora had a lot to do, and they were the stars. Too bad they were pretty boring in their previous movies.
  • Pepper: Gwenyth stole the scenes she was in just by being a better actor and presence than anyone else.
  • Black Panther, Spider-man, Doctor Strange, etc all showed up just to be there, but served no other purpose.
As a movie qua movie, the movie exists only to complete what happened in the last movie. It contained no real moral dilemmas, no real character tension, no real insights, no real inspiration or sacrifice (Black Widow's sacrifice was antiseptic and Iron Man's was accidental), and nothing really interesting story-wise other than its utter mangling and refusal to deal with the more interesting ramifications of story that was supposedly occurring around them.

Was it entertaining? If you ignore all of the parts than made my brain hurt, then it was entertaining. I wanted to see how it ended, which is about all one could have hoped for and no more. Infinity War was more entertaining and more satisfying (not that it was good, per se, but it was a better MCU movie). This was just okay.

mercredi 8 avril 2020

Space Pirate Trainer VR Free Download

Remember those awesome classic arcade cabinets? Imagine if those were immersive… Space Pirate Trainer puts you in one of those; fighting off relentless waves of droids with all the weapons and gadgets you would ever need as a space pirate. You better dodge some of those incoming lasers though, since just using your shields won't get you in the top rankings. Pick up your blasters, put on your sneakers, and dance your way into the Space Pirate Trainer hall of fame.

Space Pirate Trainer is the official trainer for wannabe space pirates in VR. Launched as one of the first titles for SteamVR/HTC Vive, Oculus Touch and Windows Mixed Reality, Space Pirate Trainer has been under continuous development on a mission to refine its gameplay and improve the overall experience. It has been widely used as one of the go-to demos for VR.

No real droids where harmed during the creation of this game.
Use your straps and stay in your VR area to make sure no humans will be harmed.

GAMEPLAY AND SCREENSHOTS :
DOWNLOAD GAME:
♢ Click or choose only one button below to download this game.
♢ View detailed instructions for downloading and installing the game here.
♢ Use 7-Zip to extract RAR, ZIP and ISO files. Install PowerISO to mount ISO files.

Space Pirate Trainer VR Free Download
http://pasted.co/af29b5ae

INSTRUCTIONS FOR THIS GAME
➤ Download the game by clicking on the button link provided above.
➤ Download the game on the host site and turn off your Antivirus or Windows Defender to avoid errors.
➤ Once the download has been finished or completed, locate or go to that file.
➤ To open .iso file, use PowerISO and run the setup as admin then install the game on your PC.
➤ Once the installation process is complete, run the game's exe as admin and you can now play the game.
➤ Congratulations! You can now play this game for free on your PC.
➤ Note: If you like this video game, please buy it and support the developers of this game.

SYSTEM REQUIREMENTS:
(Your PC must at least have the equivalent or higher specs in order to run this game.)


Minimum:
• OS: Win 7 or higher
• Processor: intel i5
• Memory: 8 GB RAM
• Graphics: GTX 970
• DirectX: Version 11
• Storage: 3 GB available space
• Sound Card: Integrated

Recommended:
• OS: Win 7 or higher
• Processor: intel i7
• Memory: 16 GB RAM
• Graphics: GTX 980 or better
• DirectX: Version 11
• Storage: 3 GB available space
Supported Language: English, Italian, Spanish, Polish, Russian, Portuguese-Brazil, Simplified Chinese language are available.
If you have any questions or encountered broken links, please do not hesitate to comment below. :D

samedi 28 mars 2020

The Talk

If I had to give a presentation to a class about my job, my profession, my possibly foolish choice of becoming a small business owner, my main concern is this: I really don't want to sound like an asshole. I say this because I didn't use to be a small business owner, so I know how I sound when I talk about state mandated wage inflation, reckless politicians in Sacramento, and our incoming tariffs from our learning disabled president. I've got enough opinions about politics and policy to really sound like an asshole, to everyone! It crosses political boundaries. I'm that good.

Maybe I am an asshole. It's always a consideration. Maybe I should consider the advice of Raylan Givens: If you meet an asshole in the morning, you've met an asshole. But if you meet assholes all day, you're the asshole.

Or maybe Master Zhuangzi. To paraphrase:

Once upon a time, I, Chuang Chou, dreamt I was an asshole, pontificating hither and thither, to all intents and purposes an asshole. I was conscious only of my irritation as an asshole, unaware that I was Chou. Soon I awaked, and there I was, veritably myself again. Now I do not know whether I was then a man dreaming I was an asshole, or whether I am now an asshole, dreaming I am a man. 

The distant memory of the man I once was, before I became an asshole, sometimes haunts me. Spending Other Peoples Money (amusingly referred to as OPM), flitting from job to job, voting based on lofty principles with no consideration of financial responsibility. Oh to be a man again.

To really be an asshole is to be seen as being somewhat greedy of spirit. This is a problem for small business owners. I regularly spend half a million dollars a year on games, and another half a million on labor, utilities, rent and other garbage. I am a rich man by individual standards, while a poor man by business standards. Surely I can be squeezed for a few more dollars, why so much complaining? When I think of putting The Man up against The Wall, I envision a legion of like minded people behind me. What I don't realize, is I am The Man. I will be put against The Wall. Chuang Chou never dreamt of that!

So class, to understand my plight, to understand whether I'm a man or an asshole, I think perhaps you need to grasp the duality of the situation, that both states are potentially true. That my survival depends on stability, that society is increasingly in a state of flux, and that my ability to flit around like a butterfly, hither and thither, is increasingly dependent on the whims of an indifferent populace and their feckless leaders. Also, STEM fields. Business is a good safety.

HOTT 52 - Battle 5 - A Final Desperate Battle

Battle 5 was fought over the weekend. The more I play, the more that setup finishes more quickly, and I remember the combat factors a lot more now. Less referring to the sheet and rules. However, each game finds me asking questions and I have a question from this week's battle below. But first, let's get to the action!

I generated both armies randomly. Both armies would consist of mostly militia and a few regular forces.

Humans
General - Sp x1
Spear (Sp) x3
Warband (Wb) x2   
Shooters (Sh) x4
Knight (Kn) x2
Orcs - defending
General - Wb x1
Warband (Wb) x3
Hordes (Hd) x2
Shooters (Sh) x3
Spear (Sp) x4

I thought about substituting fantasy elements (like Aerials, Magicians, Cleric, etc), but a toss of the dice said that wasn't happening.


I'm painting those Saxons as fast as I can to complete my Human warband elements. Hopefully they'll be done for next week's game! I don't like empty stands!

The Orc Warchief, Ib'Nuzgran, lines up his troops as a solid bunch.  He details a warband to remain behind in case the sneaky humans try to send a detachment down the road to sack their stronghold! The human commander, Major Nesbin, sees an opportunity and details his Knights to head down the road and see what trouble they can cause.


"Goblins to the front!" Ib'Nuzgran roars! The goblins rush ahead of the whip cracks from the orc sergeants, eager to taste human blood! Nesbin, seeing an opportunity to rain missile fire on the hordes, has his Shooters fold inwards as the goblins approach. The treacherous goblins then turn towards the wings, and Nesbin regretfully moves them back to keep the line intact.

Behind the goblins, the Bestials move forwards towards the approaching Human army.


The Human Shooters do their job, launching a hail of arrows on the exposed hordes. Their courage melts like snow in the sun and the goblins run away, ignoring the curses of the Orc sergeants. The lines draw close and then rush to attack! The Orc Warband drives through the Human lines, pushing their opponents back and pursuing with bloodlust!


Meanwhile, the Knights head down the road to see if they can sack the Orc stronghold. The warband left behind to guard it takes up a position in the woods near the road. The Knights are reluctant to take their hoses into the woods, so one element attempts to distract the Orcs while the other group of Knights attempts to swing around. Unfortunately, being so far away from their commander, it is hard to keep their attack organized! The Knight's attack falters as they delay in how to best approach the stronghold. (The distance is greater than 600p to their commander and the Kn are behind an impassable hill with woods - it requires 2 PIPs to move each element, instead of 1. With the battle focus on the line, as you'll see below, this is as far as the Kn got. If only the humans had a couple of better PIP rolls...)


The battle's momentum swings towards the Bestials as the Human attackers are pushed back or destroyed! However, the impetuous Orc Warchief breaks off from supporting his warband to attack the nearby Human Shooters. Recoiling from the Human's counterattack, the Orc Warlord finds himself behind the other Orc Warband, out of position should the Warband be forced to recoil! Lucky for Orcs, the warband fights on.

It turns grim for the humans. Only a Blade, the Majorand his command of Spears, and two Warbands remain of the line of Human attackers! The Bestials line is mostly intact and howling for human blood!


Nesmith sees an opportunity, however, and orders a desperate charge! The warbands and shooters surround the Orc Warchief and press the attack. The Warchief falls! The Bestials, disorganized and demoralized, retreat from the battle and their encampment. (6v1 in favor of the humans almost always guarantees a victory, as it did in this case. The odds were good for the humans for this bound, but had it not gone well, the Orcs were looking well on the way to victory.)

Humans win versus Bestials (Orcs/Goblins) (8 - 10G)

The Orc General didn't have many options when his surrounding elements were defeated, leaving him exposed. It was a close battle and with the Human line as wrecked as it was, there were going to be a lot of overlap situations when the lines closed again.

So my question came about with regards to when one element moves into contact with an enemy. For those of you who don't play HOTT/DBA (Hordes of the Things game is derived from the historical wargame De Bellus Antiquitatus), how elements contact each other and then "conform" (line up so that the elements are square with each other) is a whole set of precise rules - written in what is known as "Barkerese"! For comparison, the language (and organization) of 1st edition Advanced Dungeons & Dragons is similar to DBA/HOTT. 

My question came to who had to conform to whom, when a group contacts a group, and if supporting elements (elements in the 2nd rank that can add to the combat resolution of the elements in the front rank) also conformed. I ruled at the time in one way, but after a quick (and slightly embarrassing) newbie question/discussion posted to the HOTT Facebook group, I reread the rules and now I understand - when a group contacts a group, the conforming applies to the entire group, including supporting elements.

My shorthand for remember this is: Moving group conforms to standing group, single elements conform, otherwise, check the rules! It works for me... 

The other thing I (re)learned is that when moving through Bad Going, you move a group as a single column, or if you want to keep a line, those elements in Bad Going move as individual elements. It didn't come up this game, but has happened in previous games and I had forgotten that.

That's what I'm really enjoying, is this relearning and learning of little bits and elements. It feels just like AD&D/OD&D in that regards, and that just makes me happy.

On to Battle #6 next week!

Granblue Fantasy Versus Free Download

Granblue Fantasy has soared into the hearts of millions since its release as a browser game for smartphones in 2014, and will celebrate its sixth birthday in March 2020. Featuring Cygames' high-quality art, captivating sound design, and an ever-expanding game system, Granblue Fantasy has continued to charm its fans throughout the years.

Now Cygames has partnered with Arc System Works, known for such popular fighting franchises as GUILTY GEAR and BlazBlue, to bring Granblue Fantasy to the world of fighting games, complete with top-notch game design and one-of-a-kind 3D graphics.

GAMEPLAY AND SCREENSHOTS 

DOWNLOAD GAME:

♢ Click or choose only one button below to download this game.
♢ View detailed instructions for downloading and installing the game here.
♢ Use 7-Zip to extract RAR, ZIP and ISO files. Install PowerISO to mount ISO files.

Granblue Fantasy Versus Free Download
http://pasted.co/af29b5ae

INSTRUCTIONS FOR THIS GAME
➤ Download the game by clicking on the button link provided above.
➤ Download the game on the host site and turn off your Antivirus or Windows Defender to avoid errors.
➤ Once the download has been finished or completed, locate or go to that file.
➤ To open .iso file, use PowerISO and run the setup as admin then install the game on your PC.
➤ Once the installation process is complete, run the game's exe as admin and you can now play the game.
➤ Congratulations! You can now play this game for free on your PC.
➤ Note: If you like this video game, please buy it and support the developers of this game.

SYSTEM REQUIREMENTS:
(Your PC must at least have the equivalent or higher specs in order to run this game.)

Minimum:
• OS: Windows 7/8/10 (64-bit OS required)
• Processor: AMD FX-4350, 4.2 GHz / Intel Core i5-3470, 3.20 GHz
• Memory: 4 GB RAM
• Graphics: Radeon HD 6870, 1 GB / GeForce GTX 650 Ti, 1 GB
• DirectX: Version 11
• Network: Broadband Internet connection
• Storage: 7 GB available space
• Sound Card: DirectX compatible soundcard or onboard chipset

Recommended:
• OS: Windows 7/8/10 (64-bit OS required)
• Processor: AMD Ryzen 5 1400, 3.2 GHz / Intel Core i7-3770, 3.40 GHz
• Memory: 8 GB RAM
• Graphics: Radeon HD 7870, 2 GB / GeForce GTX 660, 2 GB
• DirectX: Version 11
• Network: Broadband Internet connection
• Storage: 7 GB available space
• Sound Card: DirectX compatible soundcard or onboard chipset
Supported Language: English, French, Italian, German, Spanish, Polish, Czech, Russian, Hungarian, Dutch, Danish, Portuguese, Finnish, Norwegian, Swedish, Korean, and Simplified Chinese language are available.